Table of Contents
A breach is not only a legal event. It can affect customer records, employee data, email accounts, shared folders, vendor access, invoices, compliance documentation, and the recovery costs required to get people working again.
That is why data breach insurance belongs beside cybersecurity planning, not in place of it. Coverage can help with financial exposure, but it does not replace MFA, patching, 1-Guard, 1-Vault, 1-SIEM, 1-DarkScan, 1-Shield, response planning, backups, monitoring, or tested recovery.
Tony Rushin, Marketing Vice President at Network 1 Consulting, notes: “Coverage helps after a claim only when the business can show its controls, response steps, logs, and recovery process were ready before the incident.”
Why Data Breach Insurance Belongs In An Operational Risk Discussion
Breach coverage has become an operations issue because the first impact lands in daily work. Approvals stop when email is locked. Payroll questions pile up. Shared drives, claims documentation, vendor coordination, and customer updates all depend on systems being available and trusted. IBM/Ponemon reports breach costs of $10.22 million for U.S. companies and $4.44 million globally.
You need to know where insurance, IT controls, and recovery responsibilities meet before a compromised account becomes a stalled billing cycle or customer communication problem.
-
Claims need evidence: Policies often require proof of controls, logs, timelines, and response actions.
-
Operations lose access: Locked accounts interrupt invoicing, project files, payroll approvals, and customer service tickets.
-
Recovery must be tested: Backups matter when restores work, including monthly 1-Vault file restore testing.
-
Security gaps affect pricing: Weak MFA, patching, endpoint protection, or logging can create renewal and claim friction.
Those details shape what a policy may help with during an interruption. MFA, endpoint protection, backup testing, incident documentation.
|
Operational area |
Evidence insurers may request |
Business owner involved |
Practical control example |
|---|---|---|---|
|
Email and account access |
MFA enrollment reports, privileged account changes, failed login alerts |
IT manager and department heads approving access restoration |
MFA through 1-Identity with SIEM alerts for unusual sign-in patterns |
|
Endpoint and server health |
Patch records, endpoint protection status, malware quarantine logs |
IT operations lead coordinating with finance or HR system owners |
1-Guard Security Suite plus documented patching for laptops and servers |
|
File recovery and shared drives |
Backup job history, restore test results, list of recovered folders |
Operations manager validating access to project files and customer documents |
1-Vault tested recovery for accidentally or maliciously deleted files |
|
Customer and vendor response |
Incident timeline, notification approvals, vendor ticket history |
General counsel, client service director, and vendor relationship owner |
Central incident documentation linking SIEM alerts, support tickets, and response actions |
|
Billing and payroll continuity |
Downtime records, restored application timestamps, workaround approvals |
Controller and payroll administrator confirming transaction completion |
Recovery runbook covering accounting software, payroll portal access, and banking approvals |
What Does Data Breach Insurance Cover During A Business Interruption
A controller sees suspicious invoice changes after a Microsoft 365 account is compromised. Finance pauses vendor payments while IT reviews mailbox rules, login history, and file access. With breach costs averaging $4.44 million per incident, the question of what does data breach insurance cover needs a practical answer, with final terms reviewed by your insurance advisor.
-
Incident response and investigation: Specialists determine what happened, which accounts were used, and what systems or records were affected. SIEM logs, MFA records, patching history, and monitored alerts help build the timeline.
-
Notification and communication costs: Coverage may support customer, employee, regulator, or partner notices. The workflow needs accurate names, data types, deadlines, and approval steps.
-
Legal and compliance support: Counsel helps interpret reporting duties and preserve documentation. That is easier when incident notes, system logs, and response actions are captured as work happens.
-
Business interruption expenses: Policies may address downtime, delayed invoicing, lost system access, and temporary workarounds. The claim depends on clean records showing when systems were unavailable and when work resumed.
-
Recovery and restoration work: Clean backups, restore testing, and validated systems determine how quickly work resumes. 1-Vault restore testing helps prove that recovered files are usable.
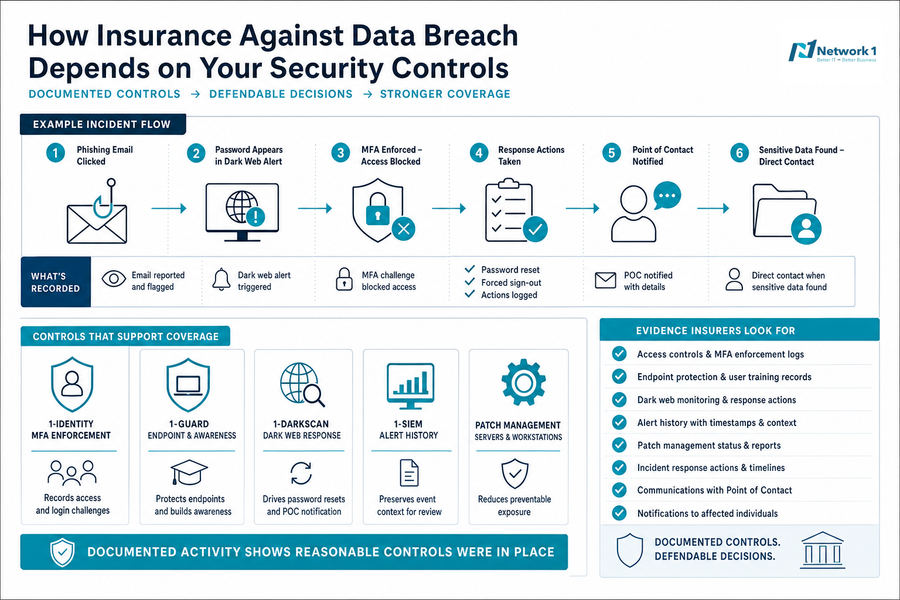
How Insurance Against Data Breach Depends On Your Security Controls
Coverage applications and claims depend on how well your organization can show that your team maintained reasonable controls. An application for insurance against data breach needs documented security activity, not a spreadsheet of tools purchased once.
What this looks like in practice: a user clicks a phishing email, then a password tied to your domain appears in a dark web alert. If MFA was enforced, the ticket shows blocked access, forced password change, Point of Contact notification, and any direct contact when sensitive personal information was found.
This matters because 25% of surveyed respondents experienced data theft or loss, and 12% were unsure if they had been breached. A claim conversation often turns on what was enforced, what alerted, who responded, and what changed afterward.
-
MFA enforcement: 1-Identity records who had access and how login challenges were applied.
-
Endpoint and awareness: 1-Guard combines endpoint protection with KnowBe4 training.
-
Dark web response: 1-DarkScan drives forced password resets and Point of Contact notification when domain passwords are exposed.
-
SIEM alert history: 1-SIEM preserves event context for review, escalation, and incident timelines.
-
Patch management: Server and workstation patching creates a history of maintenance activity.
Strengthen Your Cyber Insurance Position
Why Cyber Data Breach Insurance Cannot Replace Tested Recovery
A paid claim does not reopen email, restore shared files, bring back a line-of-business application, or give customer service the records needed for pending requests. A cyber data breach insurance policy addresses financial exposure. Tested recovery addresses whether people can work.
IBM’s report places average global breach cost at $4.88 million, but your first operational question is simpler: can we restore clean data and prove it? We perform monthly file restore tests for 1-Vault Veeam and 1-Vault NSure clients because a backup is only useful when the recovery works.
-
Backups must be restorable. Random monthly file restore testing confirms that files can be recovered after deletion, encryption, or corruption.
-
Microsoft 365 needs protection. 1-Vault O365 covers email, contacts, calendars, Teams items, SharePoint, and OneDrive with unlimited storage and retention.
-
Recovery roles need clarity. Define who approves shutdowns, password resets, insurer notice, and user communication.
-
Clean systems matter first. Restoring infected or misconfigured systems extends downtime and creates repeat issues for the same users, invoices, approvals, and customer records.
Prove You Are Ready Before a Breach
Network 1 Consulting helps align security controls, logs, backups, and recovery steps with what insurers may expect after an incident.
Insurance For A Data Breach Starts With Better Preparation
Improving breach readiness crosses IT, finance, legal, operations, and insurance relationships. The work becomes manageable when preparation creates two outputs: operational resilience and documentation for insurance discussions.
-
Compare applications to reality: Review MFA, endpoint protection, backups, logging, and training against what the insurance form says is in place.
-
Assign incident decisions: Confirm who approves device isolation, password resets, outside counsel, client communication, and insurer notification.
-
Test recovery assumptions: Validate file restores, Microsoft 365 restores, and server recovery steps before a ticket becomes an incident.
-
Close known gaps: Prioritize patching, O365 security hardening, DMARC, DKIM, SPF, Active Directory cleanup, and admin account review.
-
Plan through reviews: Use vCIO guidance or an Annual Business Review to align security, compliance, budget, and a 1-year or 2-year roadmap.
Within 30 days after signing, we inventory hardware and software, document the environment, deploy best practices, review cybersecurity controls, and begin immediate fixes. We help turn breach readiness into an executable plan across hardware, software, data, process, people, and strategy.
Contact Network 1 Consulting to compare your insurance requirements with existing controls, documentation, and recovery readiness before a compromised account becomes a paused payment run, a customer response issue, or a recovery scramble.
Explore Cybersecurity Services in Atlanta